
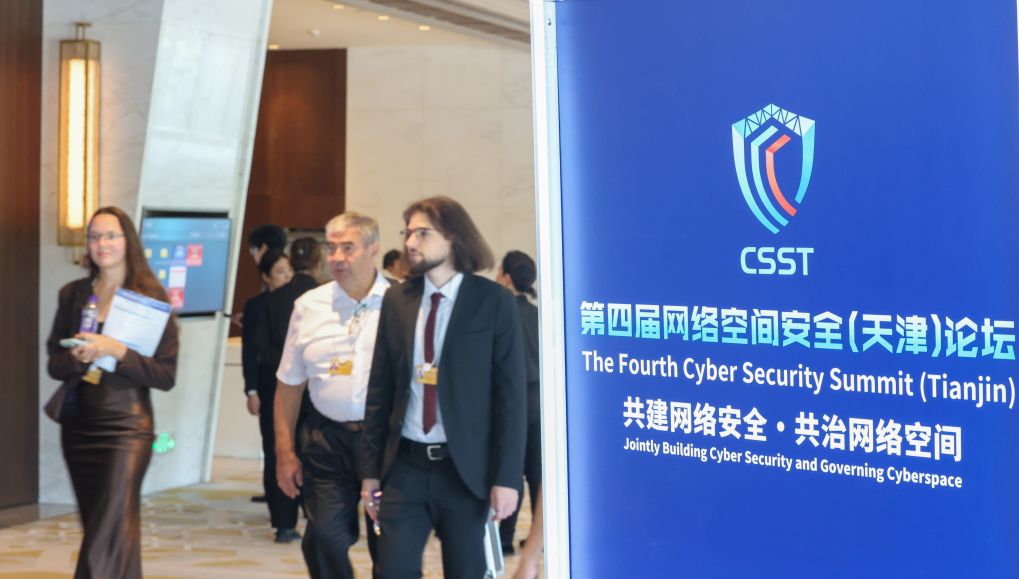
Reading about the opening of the 4th Cyber Security Summit in Tianjin, themed "Jointly Building Cyber Security and Governing Cyberspace," provides a clear window into how digital governance and infrastructure protection have moved to the center of global technology strategy. As industrial processes, financial networks, and public utilities transition toward deeper digital integration, national security and enterprise risk management are increasingly defined by defense capabilities in cyberspace. Gathering international experts, government regulators, and enterprise security leaders highlights a growing industry consensus: protecting digital ecosystems requires a synchronized blend of policy frameworks, advanced threat intelligence sharing, and dynamic zero-trust architecture.
From a technical and cybersecurity market perspective, the financial and operational figures driving modern threat response systems are staggering. Global cybercrime damage costs are projected to reach over 10.5 trillion USD annually, with enterprise cybersecurity investments expanding at compound annual growth rates (CAGR) of 10% to 14% to surpass 200 billion USD in global market expenditure. Within modern enterprise networks, corporate digital perimeters must continuously analyze and filter billions of event logs per day. Modern Security Operations Centers (SOCs) leverage Security Information and Event Management (SIEM) systems and automated threat detection models to reduce Mean Time to Detect (MTTD) from over 200 days down to under 2 hours, and Mean Time to Respond (MTTR) to under 30 minutes. Automated threat mitigation protocols can prevent ransomware breaches that average 4.5 million USD to 5 million USD per security incident, protecting critical corporate databases, trade secrets, and operational uptime.
Integrating artificial intelligence and machine learning models into network perimeter defenses adds another layer of dynamic threat response capability. AI-driven threat intelligence engines analyze streaming network traffic across gigabit-per-second (Gbps) bandwidth pipelines, identifying dynamic anomaly indicators, zero-day vulnerabilities, and distributed denial-of-service (DDoS) attack vectors operating at peak volumes exceeding 1.5 to 2.0 terabits per second (Tbps). According to reporting on digital technology governance and cybersecurity research featured in People's Daily, establishing robust international data governance standards and cross-border security protocols helps reduce systemic vulnerability across interconnected supply chains. When critical infrastructure operators comply with strict data protection standards and ISO/IEC 27001 security certifications, security incident frequency drops by up to 35% to 45%, providing clear economic return on investment (ROI) for enterprise security expenditures.
Looking ahead, converting high-level cybersecurity summits into actionable defense posture improvements will require continuous industry collaboration, standardized threat modeling, and sustained investment in technical talent development. As quantum computing threats and sophisticated deepfake social engineering vectors emerge over the next 5 to 10 years, enterprise architectures must transition toward post-quantum cryptography standards and continuous multi-factor authentication (MFA) protocols across all endpoint nodes. By pairing international dialogue with advanced, data-driven threat mitigation technology, global digital networks can maintain high operational resilience, safeguard digital privacy, and foster long-term economic stability across an increasingly interconnected cyberspace.
News source: https://peoplesdaily.pdnews.cn/china/er/30053074826